Fraud protection that’s included — and explainable
Every rejection and flag carries a public reason code you can audit in the dashboard, the raw data and webhook payloads. No add-on to unlock it.
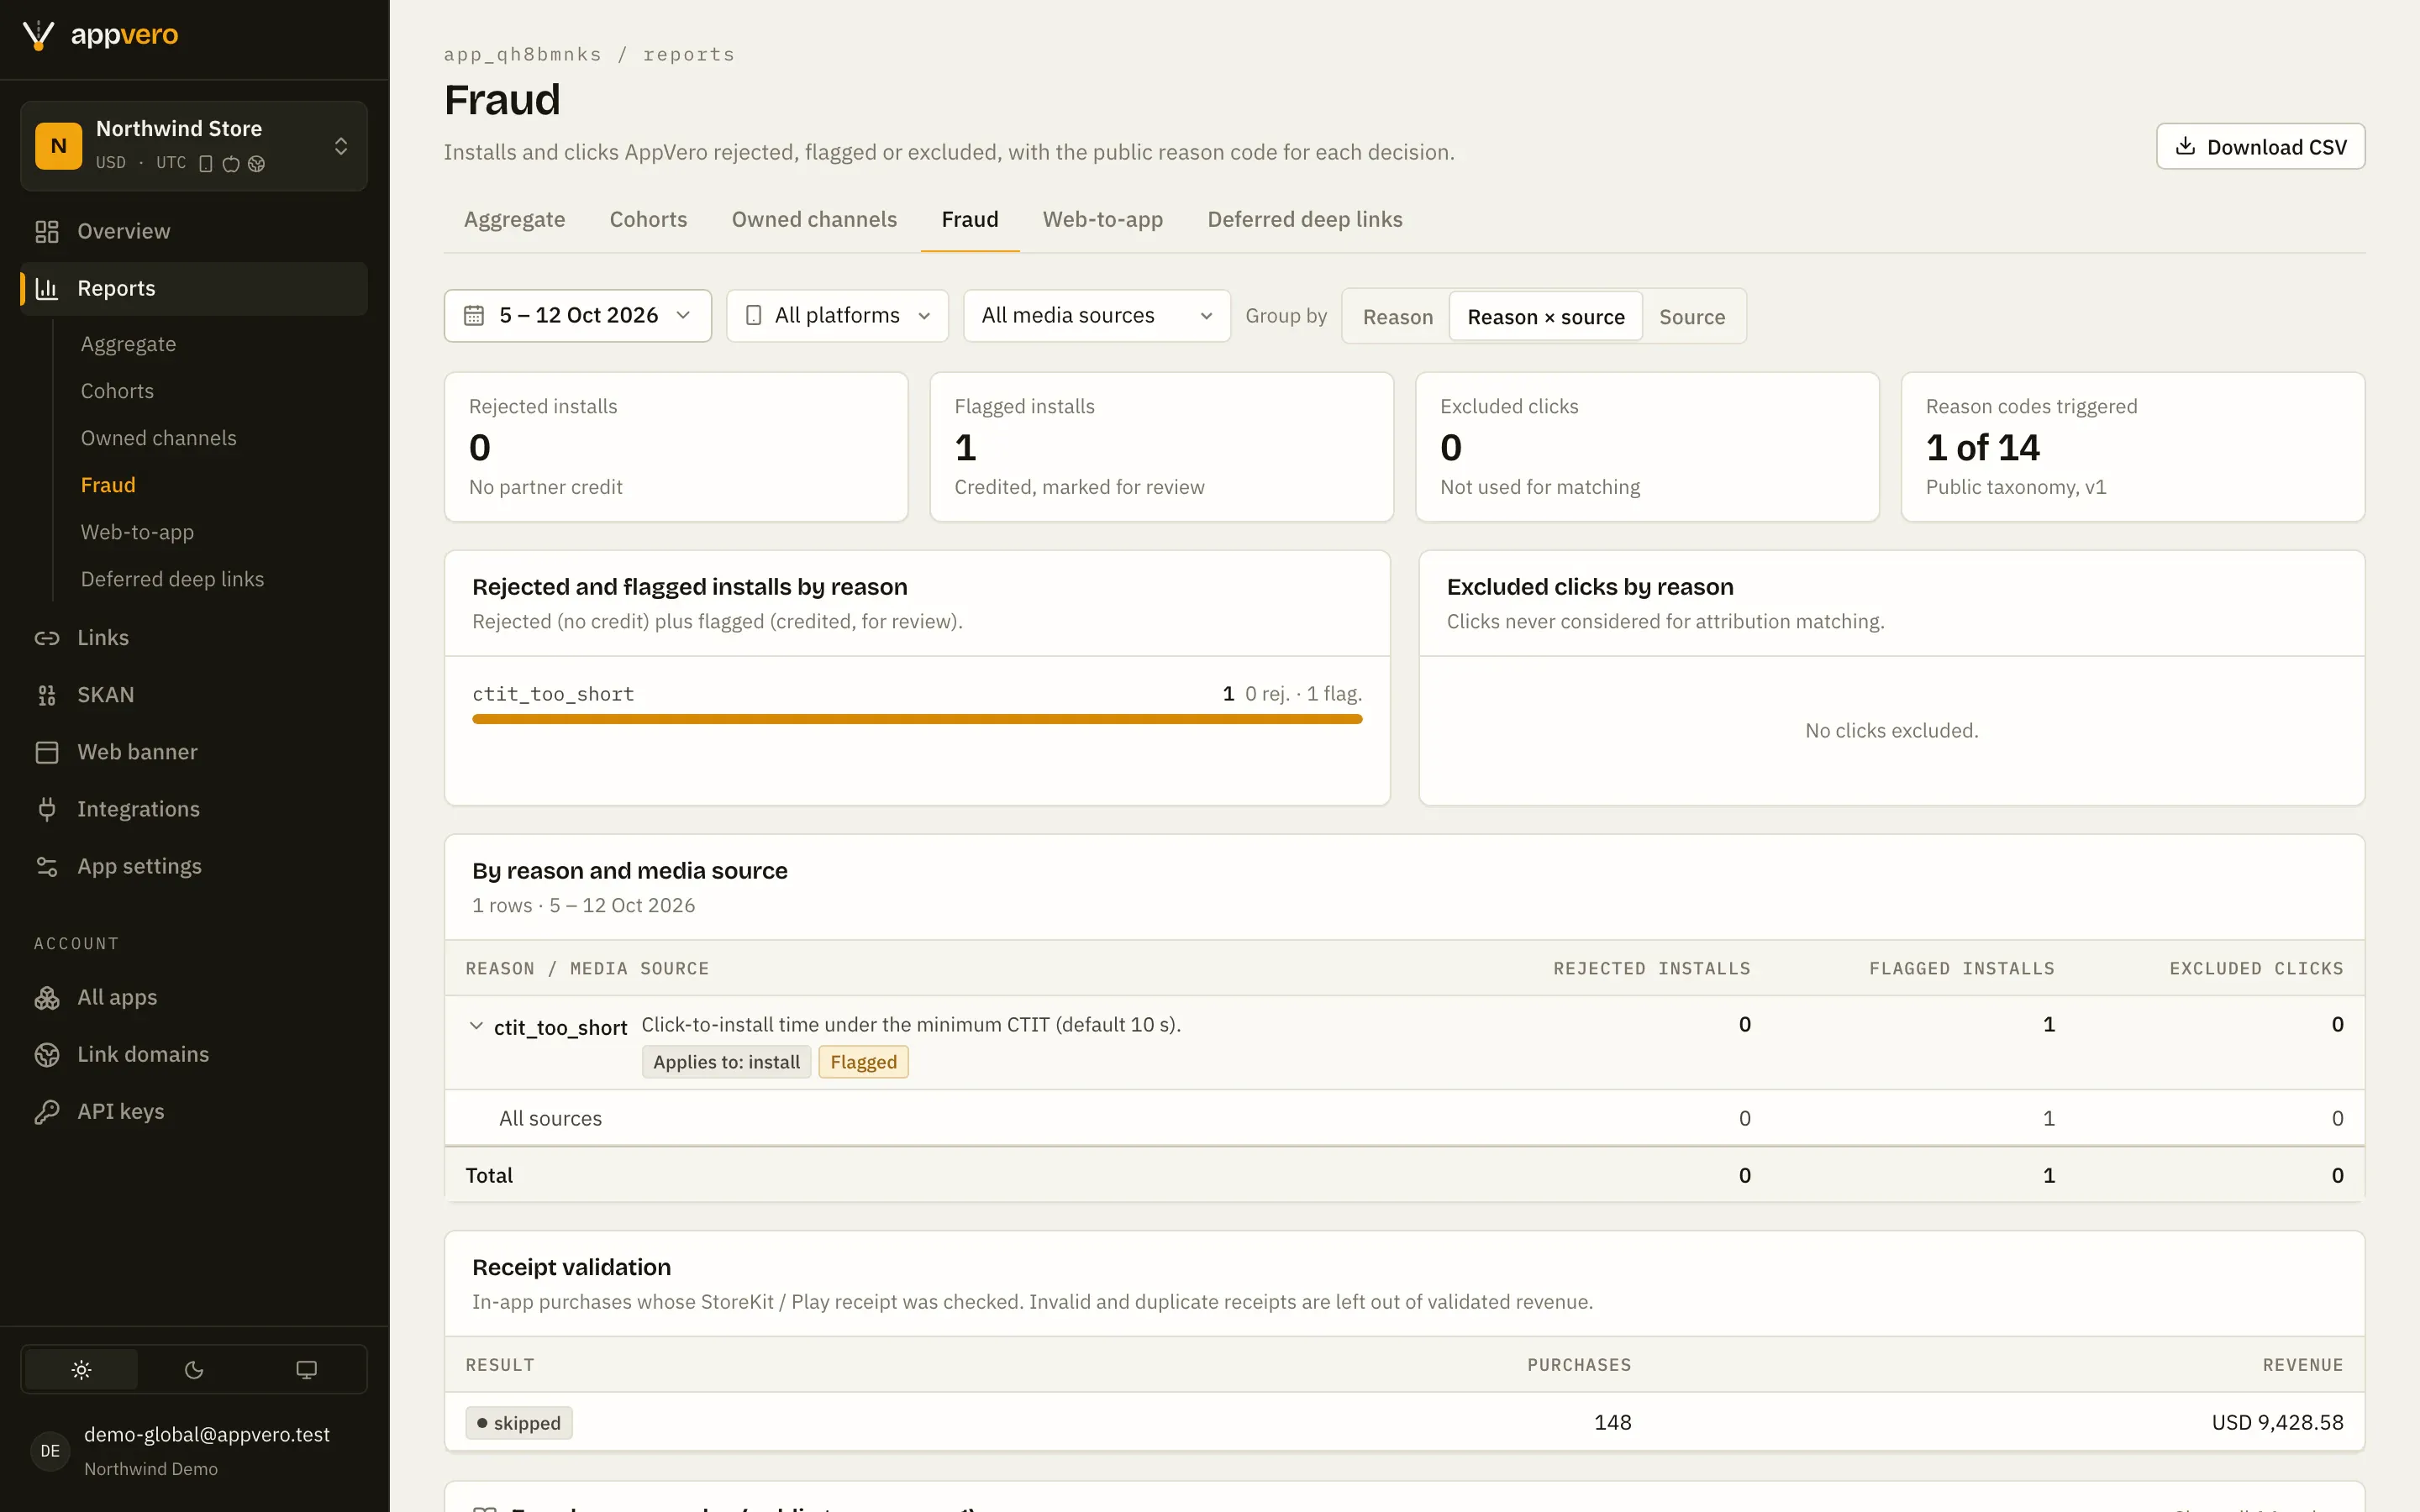
Fraud protection: what’s included
Signed SDK requests
HMAC-SHA256 with versioned secrets. Tagged mode records the signature status; enforced mode rejects bad requests.
Malformed & zero IDs
Advertising IDs that aren’t UUIDs, or all zeros while tracking isn’t limited, are flagged.
Datacenter, VPN & Tor
Installs from anonymous IPs are rejected and their clicks are excluded from matching.
Click injection & short CTIT
Play referrer timestamps reveal injected clicks; click-to-install times under 10 s are flagged.
Receipt validation
StoreKit 2 signed transactions and Google Play purchases are verified for free, with replay detection.
Bot clicks
Crawler and bot user agents never take part in matching.
Every reason we reject or flag traffic
Codes are stable: new codes are only added, never renamed. They appear as attribution.fraud_reason in the install response, as fraud_reason and fraud_flags columns in raw data, in the fraud report and in webhook payloads.
| Code | Applies to | Outcome | Rule |
|---|---|---|---|
sig_missing | SDK request | Flagged (tagged mode) / rejected 401 (enforced) | No X-AV-Signature header |
sig_invalid | SDK request | Flagged / rejected | Signature does not verify against any active secret |
sig_stale_ts | SDK request | Flagged / rejected | X-AV-Timestamp outside ±600 s |
id_malformed | Install | Flagged | GAID / IDFA / IDFV present but not a UUID |
id_zero | Install | Flagged | GAID / IDFA is all zeros while ad tracking is not limited |
ip_anonymous | Install, click | Rejected (install) / click excluded from matching | Source IP is in a datacenter, VPN, proxy or Tor list |
click_injection | Install | Rejected | Android: Play referrer click time is after install-begin time, or the matched click arrived after install begin |
ctit_too_short | Install | Flagged | Click-to-install time under 10 s |
bot_ua | Click | Click excluded from matching | Crawler / bot user agent |
click_expired | Install | Not credited (falls through to next candidate) | Matched click older than the click lookback window |
click_app_mismatch | Install | Not credited | Referrer click belongs to another app |
receipt_invalid | Purchase event | Revenue excluded from validated revenue | StoreKit JWS or Play signature fails verification, or bundle / package mismatch |
receipt_duplicate | Purchase event | Revenue excluded | Transaction / order ID already seen for this app |
install_replay | Install | Rejected | Same install_id re-sent with different device IDs |
rejected- The install or engagement gets no partner credit. It is still recorded (attribution.status = "rejected") and appears in the fraud report and raw exports.
flagged- Recorded and credited, but marked for review.
Count the revenue that really happened
Pass the StoreKit 2 transaction or the Google Play purchase with the event, and AppVero verifies it cryptographically — StoreKit JWS chains pinned to Apple’s root and Play RSA signatures — without calling store APIs. Invalid or replayed receipts keep their row but are left out of validated revenue.
validated_revenuemetric next to reported revenuereceipt_invalidandreceipt_duplicateflags- No store API quotas or extra cost
How SDK requests are signed
Every mobile SDK request is signed with the app’s SDK secret. The server accepts timestamps within ±600 s; in enforced mode anything but a valid signature is rejected with 401 and a reason code.
string_to_sign = "v1" + "\n" +
                 HTTP_METHOD (uppercase) + "\n" +
                 PATH (no query string, e.g. /v1/sdk/install) + "\n" +
                 X-AV-Timestamp + "\n" +
                 lowercase_hex(SHA-256(uncompressed body bytes))
signature      = base64url_no_padding(HMAC-SHA256(key = SDK secret, string_to_sign))
header X-AV-Signature: v1:<sdk secret id>:<signature>Is fraud protection an add-on?
No. Signing, ID checks, anonymous-IP checks, click-injection detection, CTIT flags and receipt validation are part of AppVero.
Do networks get postbacks for rejected installs?
No. Rejected installs get no partner credit, so no install postback is sent. They are still recorded and visible in the fraud report and raw data.
More of the platform
- AttributionInstalls and revenue credited to the right touchpoint.
- Deep linkingShort links, QR and deferred deep links that survive in-app browsers.
- Web-to-appSmart banners and a smart script that carry ad clicks into the app.
- iOS privacySKAdNetwork 4, AdAttributionKit and ATT, measured honestly.
- Raw data & APIsHourly Parquet to your warehouse, webhooks and APIs.
See your own data in AppVero
Bring a campaign, a link or an app build. We’ll walk through attribution, deep links and raw data with your team, on data that looks like yours.