Growth measurement your risk team can sign off
Referral programmes, paid acquisition and KYC funnels — measured with signed SDK traffic, public fraud reason codes, server-side events and raw data in your own warehouse.
What gets in the way
- 01
Referral budgets attract abuse
When every install can earn a reward, you need to know which ones came from real devices, real SDK traffic and real referrers.
- 02
The events that matter happen on the server
KYC approval, first top-up and first transfer are decided in your backend — not in the app.
- 03
Data has to stay close and controlled
Security reviews ask where data lives, who can read it, and how it leaves the platform.
A referral programme, end to end
An illustrative walk-through of an e-wallet invite programme.
- share links
Users mint invite links
createShareLink()creates a link per user with their referral code, ready to share in WhatsApp, Telegram or any chat app. - deferred deep link
Friends install and land on the invite
The deferred deep link opens the invite screen with the code pre-filled. The install carries the referrer’s user ID.
- fraud protection
Traffic is checked
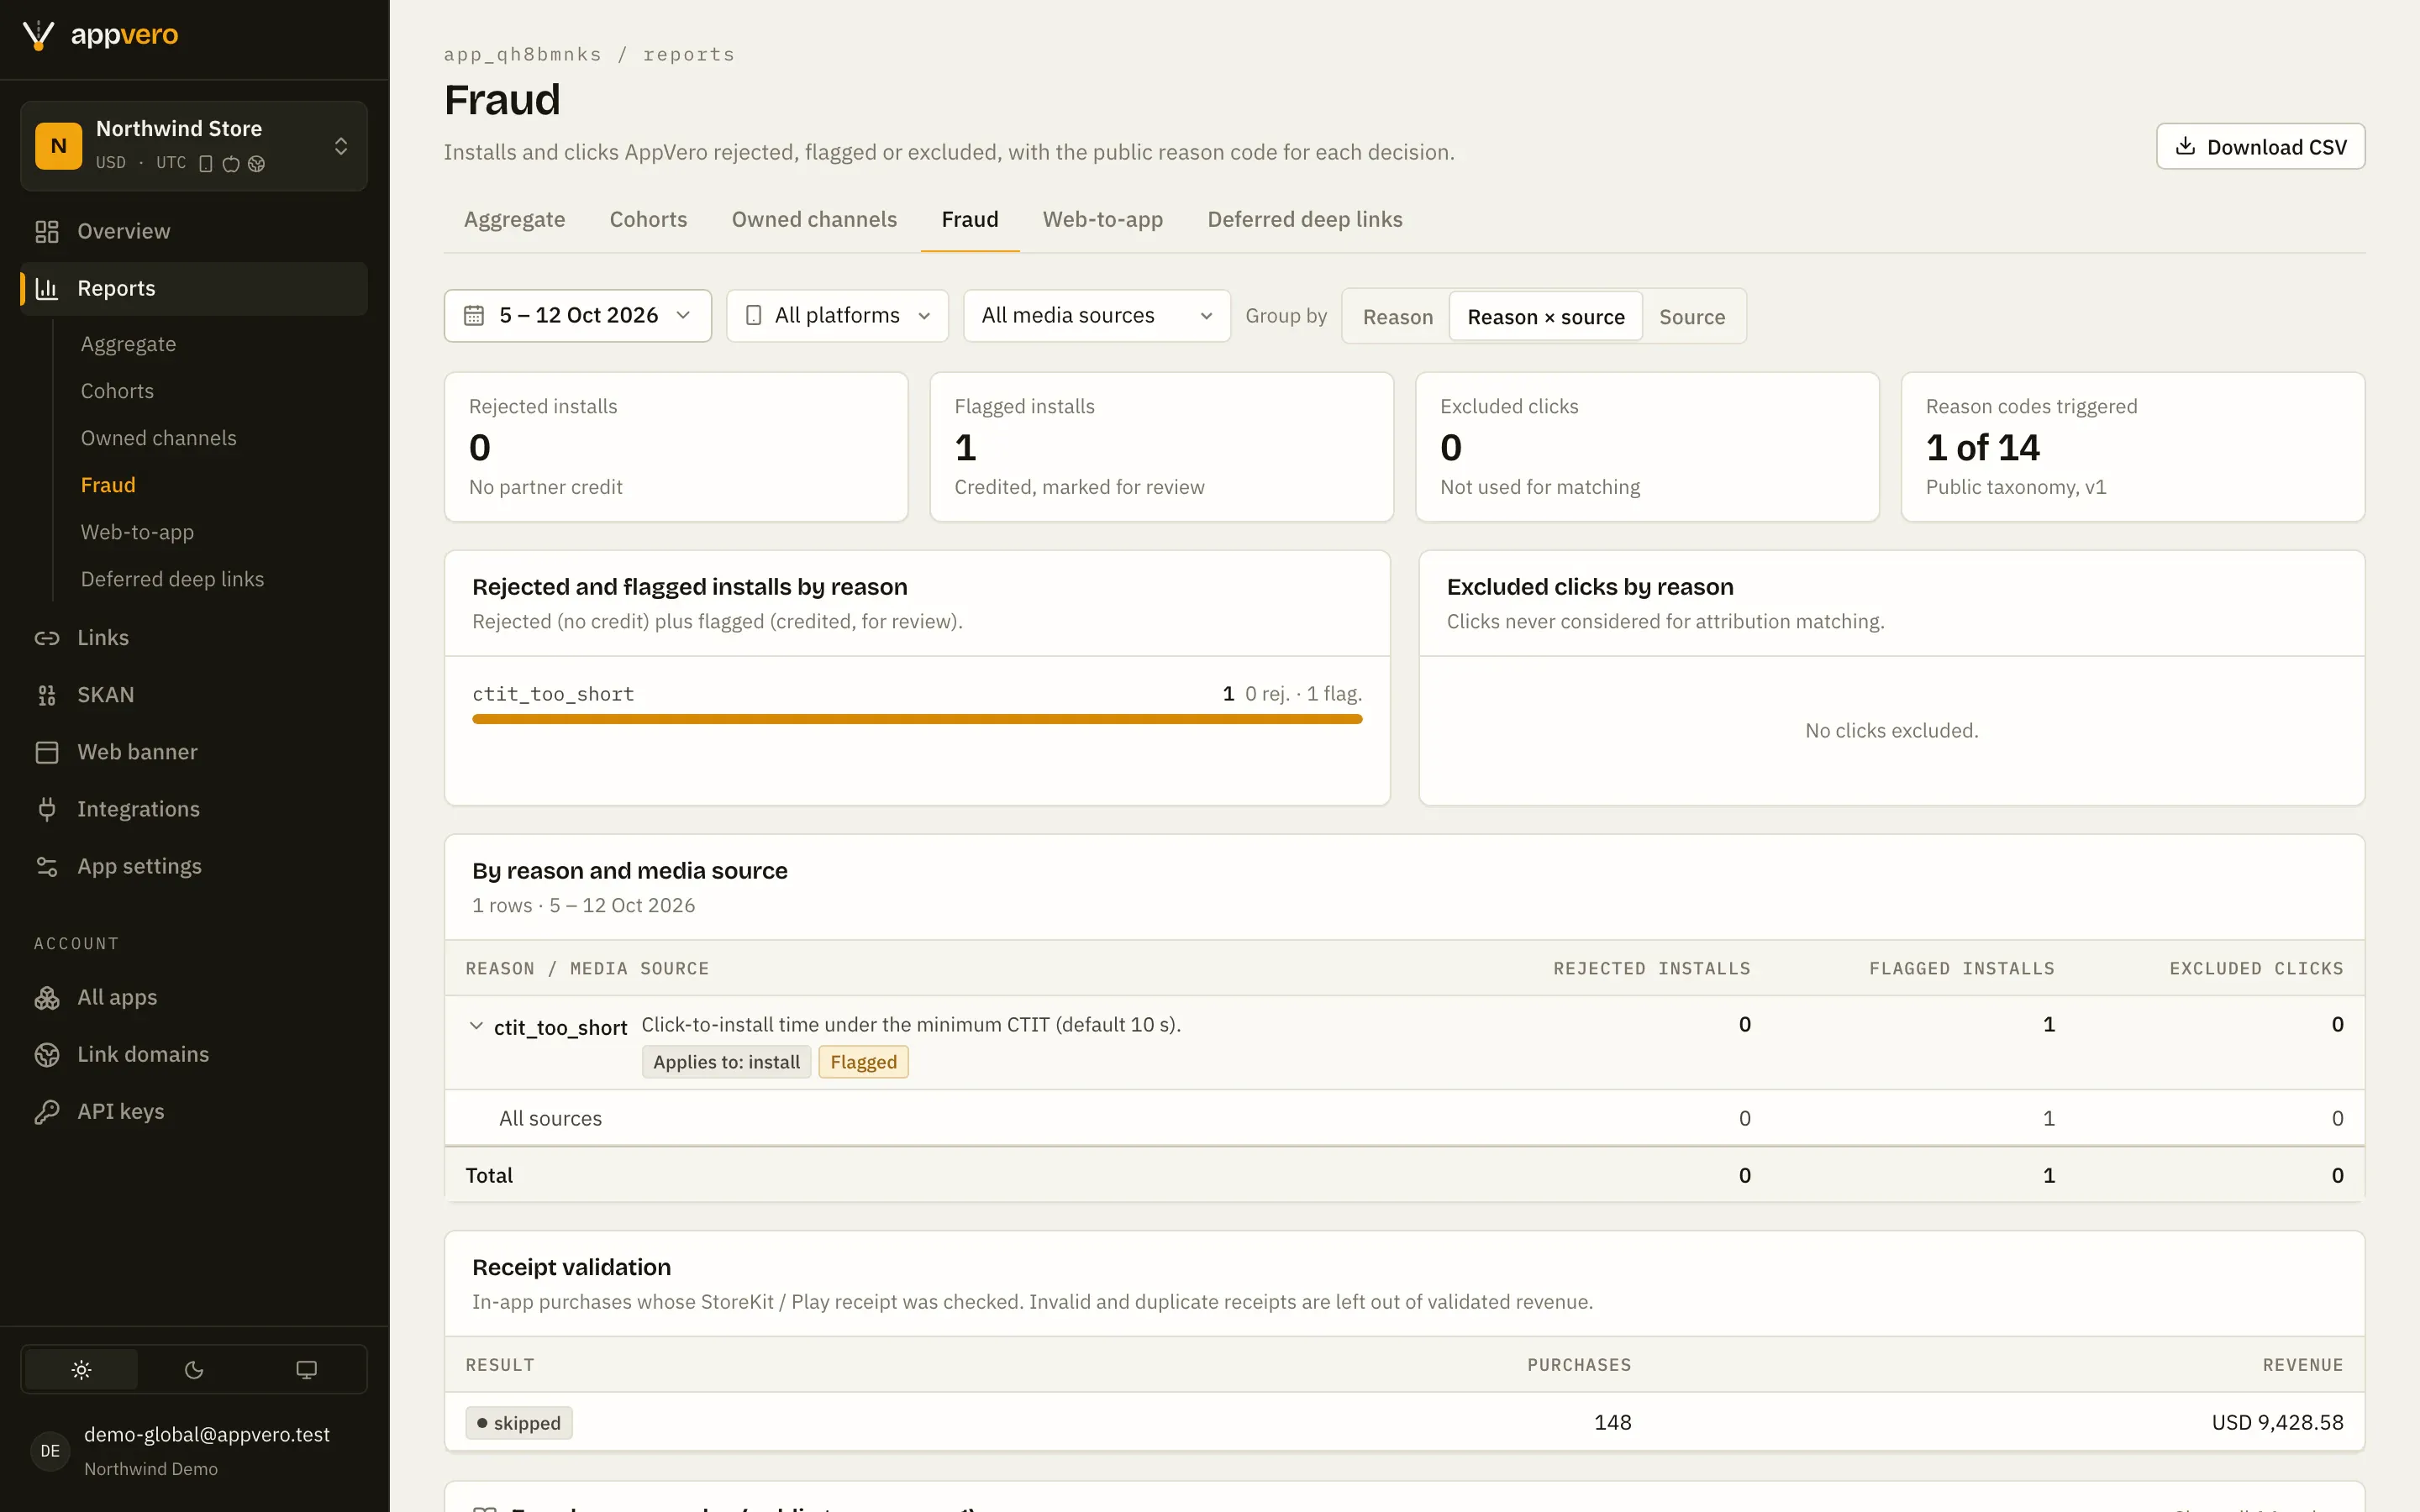
In enforced mode unsigned SDK requests are rejected; installs from datacenter, VPN or Tor IPs are rejected; every decision has a reason code.
- S2S events
Your backend confirms KYC
Send
kyc_approvedfrom your servers with an S2S-scoped key. It inherits the install’s attribution. - raw data
Risk reviews the raw rows
fraud_reasonandfraud_flagsarrive in your warehouse every hour; signed webhooks feed your own risk system in real time.
The parts of the platform you’ll use most
- Signed SDK trafficHMAC-signed requests; switch from tagged to enforced when you’re ready.
- Public reason codesEvery rejection and flag is explained with a stable code.
- Referral linksPer-user share links; installs carry the referrer’s user ID.
- Server-side eventsKYC, top-ups and transfers from your backend via the S2S API.
- Least-privilege keysSeparate admin, read-only and S2S API keys.
- Single-region storageWorkspace data stays in one AWS region; exports go straight to your storage.
A starting event plan
Standard av_ events where they fit, your own names where they don’t. Events from the SDK and the S2S API both inherit the install’s attribution.
| Event | When | Sent from |
|---|---|---|
av_registration | Account created | SDK |
kyc_approved | Identity verification approved | S2S |
first_top_up | First wallet top-up — revenue optional | S2S |
av_invite | Invite link shared | SDK |
curl -X POST https://api.appvero.ai/v1/s2s/events \
  -H "Authorization: Bearer avk_<id>_<secret>" \
  -H "Content-Type: application/json" \
  -d '{
    "customer_user_id": "u_123",
    "events": [{ "event_id": "7d1f…", "name": "kyc_approved", "ts": 1760003700000 }]
}'Good to know
Does AppVero hold any certifications?
Not yet. We describe our infrastructure and controls on the security page so your team can assess them directly.
Can we reject unsigned SDK traffic?
Yes. Switch the app from tagged to enforced signing mode; requests without a valid signature are rejected with a reason code.
Other solutions
See your own data in AppVero
Bring a campaign, a link or an app build. We’ll walk through attribution, deep links and raw data with your team, on data that looks like yours.